
Secure E-signatures Therapy: Secure E‑Signatures Therapy
Last Updated on October 24, 2026
How Secure E‑Signatures Therapy Accelerates Consent
Adding Secure e‑Signatures Therapy to your workflow cuts the time it takes for a new client to sign a treatment agreement from days to minutes. Your practice manager won’t wait for mailed forms or schedule a paper-heavy review anymore. Instead, a patient gets a single link, authenticates with a PIN, and the signed document lands right in their client folder, ready for billing.
In traditional private Practices, onboarding friction often delays initial consultations. Clients reaching out for psychological support are often vulnerable or distressed. Forcing them to print, scan, mail forms, or download external PDF viewers creates unnecessary hurdles. Modern digital authorization removes this friction, building an empathetic, efficient client experience from day one.
Why Do Therapists Need Secure E‑Signatures?
Paper has three big weaknesses: loss, illegibility, and slow processing. The health-care industry is tightening its compliance demands. A HIPAA violation can cost a practice more than a fine—it can destroy reputation and client trust. Secure e‑Signatures keep documents in a tamper-evident chain of custody while meeting the HHS guidance on electronic Signatures and HIPAA compliance.
Beyond regulatory penalties, clinicians carry serious ethical obligations. You must ensure informed Consent is authentic, fully understood, and accurately recorded. Physical papers in filing cabinets are vulnerable to damage, unauthorized staff access, and misplacement during office moves. A cryptographically verified digital signature confirms the signer’s identity and locks the document against post-signing changes.
Legal Frameworks: ESIGN, UETA, and HIPAA Alignment
When you adopt digital Consent, you need to understand the legal standards that govern electronic documents in behavioral health. Electronic agreements operate under two primary federal and state statutes in the United States, along with strict health privacy rules:
- The Electronic Signatures in Global and National Commerce (ESIGN) Act: Federally, this law confirms that electronic contracts, agreements, and Signatures carry the same legal weight as traditional pen-and-paper Signatures. This holds true as long as intent and Consent are clear.
- The Uniform Electronic Transactions Act (UETA): Adopted by nearly all states, UETA harmonizes electronic transaction laws. It sets clear criteria for record attribution, document integrity, and retention.
- HIPAA Security and Privacy Rules: Unlike general commerce agreements, behavioral health Documentation handles Protected Health Information (PHI). This requires specific safeguards. You need end-to-end encrypted transmission, strict role-based access controls, and immutable audit trails for Signatures – showing IP addresses, timestamps, and identity verification.
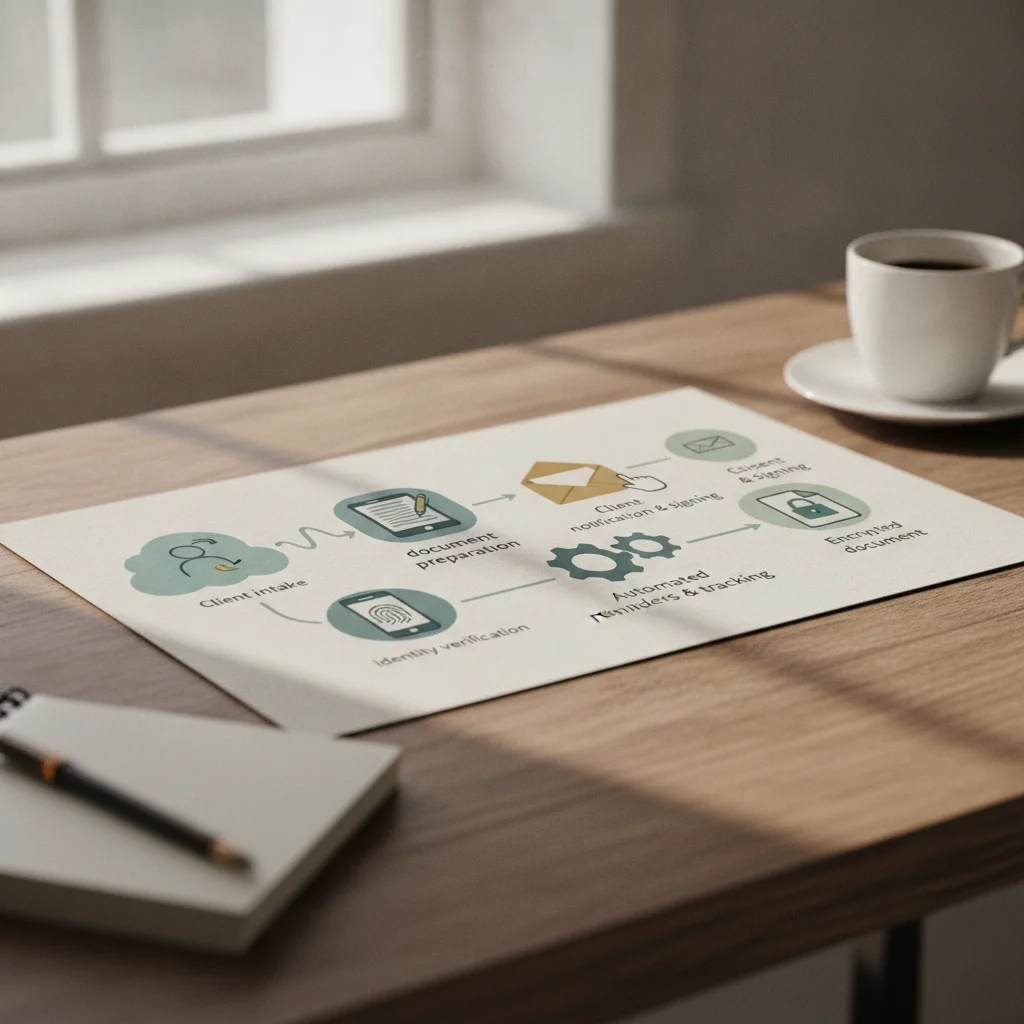
Step‑by‑Step Workflow: From Template to Archive
- Create a Consent template in Hypnotes. Drag and drop the standard Therapist Consent Form; add custom fields if you need them.
- Define signature fields – set one for the client, one for the therapist. Enable “Require authentication” so the client must log in before signing.
- Set an expiration window of 7 days. This balances urgency with client flexibility and automatically flags overdue forms.
- Send via the client portal. We generate a single email link. The client clicks, verifies identity, signs, and gets an instant confirmation.
- Track status in real time. Your dashboard shows “Pending,” “Signed,” or “Expired.” We can send alerts to the practice manager if a form lingers.
- Archive the signed PDF in the client’s record. The system automatically tags and makes the file searchable.
- Generate a compliance audit trail for the month. You can export the audit log for internal review or a potential audit.
Every step eliminates a manual touchpoint and locks in HIPAA‑ready security.
Common Mistakes and How to Avoid Them
- Skipping authentication: A form anyone can sign defeats HIPAA’s integrity requirement. Always enforce a login or two-factor verification.
- Neglecting expiration dates: Forms that sit indefinitely on a server can be revoked later. Set a clear deadline and let the system auto-flag them.
- Using generic email Signatures: These aren’t cryptographically signed and people can spoof them. Let the built-in engine generate your signature.
- Ignoring audit logs: You might think the system keeps records, but the logs are often hidden in the backend. Export monthly logs and store them in your compliance folder.
- Failing to countersign promptly: Many treatment agreements and individualized treatment plans require clinician countersignatures. If you don’t complete your portion, records remain legally incomplete for payer audits.
- Overlooking document versioning: When you update practice policies, cancellation rules, or privacy notices, ensure active clients sign the updated versions. Older historical agreements should remain untouched in the archive.
Paper vs. Secure E‑Signatures Therapy: A Side‑by‑Side Look
| Aspect | Paper Process | Secure E‑Signatures Therapy |
|---|---|---|
| Time to Signature | 3–5 business days | Under 5 minutes |
| Compliance Risk | Lost documents, illegibility, manual errors | Audit‑ready, tamper‑evident chain |
| Cost Per Signature | $0.50 (printing, mailing) | $0.02 (software overhead) |
| Environmental Impact | Paper waste | Zero paper |
| Accessibility | Requires in‑person visit | Client signs from any device |
Worked Examples: Streamlining Complex Clinical Cases
Let’s look at how Secure digital signing works across various mental health disciplines with a few scenarios.
Hypothetical Case 1: Multi-Party Consent in Couples Therapy
Imagine an outpatient practice setting up an intake for a couple starting relationship counseling. With standard paper, both partners must attend an office session just to review and sign mutual disclosure authorizations. Or, forms get physically exchanged back and forth, adding delays.
- The Setup: The clinician prepares an intake packet. This includes an Informed Consent for Couples Therapy, a Mutual Non-Disclosure Agreement, and a Telehealth Authorization.
- The Execution: The system assigns two separate recipient roles: Partner A and Partner B. Each gets distinct email addresses and unique authentication pins.
- The Flow: Partner A receives an invite, verifies their identity, signs on their mobile device during a lunch break, and submits. The system then automatically routes the updated, partially executed document to Partner B, who reviews and signs that evening.
- The Outcome: Both Signatures are securely time-stamped. A cryptographic hash confirms the document cannot be edited. The fully signed agreement is archived in the shared family file before their first joint intake session begins.
Hypothetical Case 2: Adolescent Treatment and Custodial Sign-Off
In another scenario, a solo practitioner is onboarding a 15-year-old minor client for cognitive behavioral Therapy. State laws require the parent or legal guardian to provide informed financial and clinical Consent, while the minor reviews an adolescent assent form.
- The Setup: The practice initiates a sequential workflow. The legal guardian receives the comprehensive Financial Policy, HIPAA Privacy Notice, and Parental Consent Form first.
- The Execution: Once the guardian verifies identity and signs, the adolescent assent document goes to the minor during the preliminary meeting or securely via the portal with parental oversight.
- The Outcome: The practice retains an unalterable audit log. This links the parent’s IP address, verified email, and digital signature, eliminating custody-related compliance ambiguities before clinical intervention begins.
Integrating Secure E‑Signatures with Billing and Telehealth
Once a Consent form is signed, Hypnotes automatically pushes the authorization to your billing module. The payer’s electronic claim system receives a signed attachment, reducing claim denials tied to missing Consent. Telehealth visits that start with a signed Consent are recorded in the session notes, and that same signature can serve as the signed Consent for telehealth required by many insurers.
When electronic document management links directly to session scheduling and invoicing, clinicians avoid the fragmentation common to third-party signing tools. You won’t download completed forms from an external vendor and manually upload them to your EHR. Instead, automated integration stores records right in the client chart. This keeps clinical, financial, and regulatory records perfectly synchronized.
Real‑World Impact: A Hypnotes User Experience
Think about Maya, a therapist who manages 120 clients a year. Before Hypnotes, she spent 12 hours weekly on paperwork, chasing Signatures, and re-issuing forms. After adopting our built-in Secure e-signature engine, her paperwork time dropped to 3 hours, freeing 9 hours for direct client care. Her practice’s average claim denial rate fell from 8% to 2% within three months. Maya reports that her clients appreciate the instant confirmation and the ability to sign from home.
Secure e‑Signatures Therapy reduces administrative load, cuts claim denials, and keeps your practice compliant.
Best Practices for Form Organization and Document Security
To get the most out of electronic Signatures, you need disciplined organization within your clinical software. Structured administrative protocols guarantee your files stay defensible during any insurance audit or licensing board review:
- Maintain Standardized Template Bundles: Group your required onboarding forms into logical packets (e.g., General Adult Intake, Child & Adolescent Assent, Telehealth Consent, Release of Information). This prevents you from missing critical attachments.
- Automate Periodic Renewal Requests: Standard releases of information (ROIs) typically carry an annual expiration. Configure your document system to alert staff thirty days prior to expiration so you can issue renewals effortlessly.
- Restrict Internal User Permissions: Enforce role-based access controls within your practice. Only authorized clinical staff and billing managers should review signed medical releases and confidential agreements.
- Review Audit Trails Periodically: Conduct routine internal reviews of signature certificates. Confirm that IP tracking, email verifications, and timestamps consistently function as intended.
How to Get Started: 14‑Day Free Trial
Ready to see the speed-up for yourself? Sign up for a Hypnotes pricing plan and activate the Secure e‑Signatures feature in the demo environment. No credit card required. The platform is fully HIPAA compliant right out of the box. Your practice can start signing in minutes.
Frequently Asked Questions
What exactly does Secure e‑signature mean for my patients? It guarantees that the signature is electronically signed with encryption, verified identity, and a tamper‑evident audit trail that meets HIPAA requirements.
Can I still use paper Signatures if I prefer? Yes, but using them alongside Secure e‑Signatures creates a hybrid workflow that still offers the benefits of digital Signatures while accommodating patient preferences.
Will the e‑Signatures be accepted by insurance companies? Most major insurers accept HIPAA‑compliant electronic Signatures. Hypnotes’s Signatures meet the federal guidance, giving you confidence in compliance.
How do I ensure patient privacy during the signing process? Hypnotes uses end‑to‑end encryption, role‑based access controls, and two‑factor authentication to protect patient data during signing.
Is there a limit to how many forms I can send? No. The system scales with your practice size; you can send unlimited forms as long as you remain within your subscription tier.
Are electronic Signatures legally binding for Release of Information (ROI) forms? Yes. Under HIPAA, ESIGN, and UETA regulations, an electronic signature on an ROI document is fully binding provided the patient’s identity is verified and the scope of information disclosure is clearly defined.
What happens if a client cannot sign from a desktop computer? Modern Secure e-signature tools are completely mobile-responsive. Clients can securely open the link, authenticate, read the Documentation, and draw or type their signature using any smartphone, tablet, or laptop browser without downloading extra software.
How does a practice prove that a document was not altered after signing? Every finalized document is generated with an encrypted digital certificate and a cryptographic hash. Any subsequent alteration to the document invalidates the certificate, providing clear, tamper-evident proof of document integrity.
Can multi-therapist group Practices route forms to specific supervisors? Yes. Group Practices can configure dynamic routing so that supervisee documents or specialized assessments automatically route to the designated clinical supervisor for countersigning before final archiving.